An Overlooked Mainframe Security Concern
Ask a mainframe security team what keeps them up at night, and you'll hear about RACF rule sprawl, dormant privileged IDs, or the next vulnerability in a TN3270 emulator. You'll rarely hear about the workload scheduler quietly orchestrating everything else. The IWS, however, coordinates and runs process executions, often in the millions, that touch everything from payroll and settlement to every batch job that keeps a business solvent overnight.
That makes the integrity of scheduler definitions an integral part of the cyber security plan. The question then becomes: what happens when someone changes the schedule itself?
Outside Attacks are not the Only Attacks on a Business
Most security investment goes toward keeping people out of sensitive areas using access control, encryption, intrusion detection, etc. Obviously this is the right instinct for external attackers, but it's the wrong model for someone who already has legitimate scheduler admin rights.
A compromised privileged account or simply an administrator under pressure doesn't need to breach anything. They need to edit an application description, delete a special resource, alter a run cycle, or change a dependency. Nothing about that looks like a reason to raise the alarm, but it still changes something that could disrupt critical processes.
As a result, IT teams often go into lengthy firefighting mode, trying to assess what changed and how they can safely restore it to its previous state.
Whatever the intent, the incident-response problem is the same:
What changed?
What did it look like before?
How do we safely put it back?
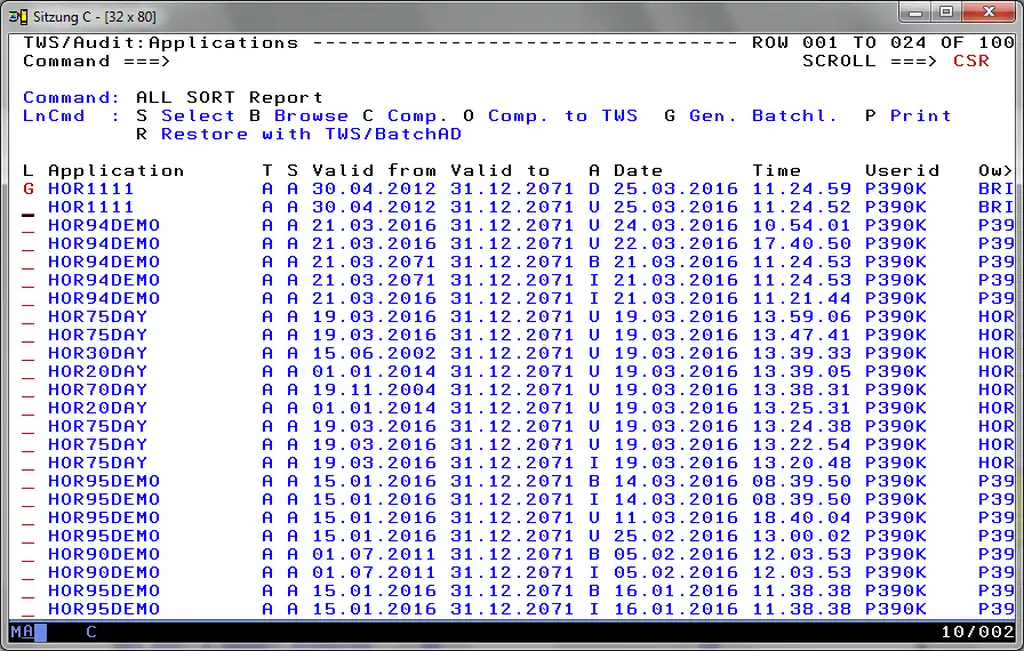
Check the User ID to see who made the change
Access Control Only Answers Half the Question
IWS provides its own controls against unauthorized access, but that only confirms whether someone was permitted to make a change and not what happens after. Scheduler definitions are deeply interconnected, and one small, authorized change can ripple outward in ways that surface only later.
Most businesses have some visibility into scheduler changes, such as a track log here, a JES output there. However, this creates a broader challenge: recovery and restoration. Knowing an object was altered at 2:14 AM doesn't help if it's since been deleted outright with nothing left to compare, if you need to prove what changed rather than just that something changed, or if you need last week's known-good version back in production now, not hand-rebuilt from memory.
That's the gap between logging and control. Logging tells a story after the damage is done. Control lets you fight back quickly.
Pro Tip
Implement regular, automated comparison reports between your current IWS definitions and a known-good baseline to proactively detect unauthorized or erroneous changes before they impact production.
An IWS/Audit Built for the Mainframe Scheduler
This is the gap IWS/Audit is built to close. Part of Beta Systems' IWS Tools suite, it captures every version of every change to IWS's definition databases, the Current Plan (CP), the Long Term Plan (LTP), and the JCL (JS) for analysis and reporting. It shows not just that a change occurred, but the full prior state of the object. It can then help you roll back to a previous revision level even if the object has been deleted.
With these IWS/Audit tools, changes survive deletion. Deletion is often the last step someone takes to cover their tracks (even unknowingly). IWS/Audit keeps history independent of the live object's survival, and can generate the batchloader statements and IWS/BatchAD control cards needed to restore a definition even after it's gone.
It’s also often the case that rollback isn't automatically safe. Schedulers manage interconnected processes, so restoring an old definition without checking its relationships can trade one outage for another. That's why version history, comparison (see image below), and impact analysis must work together to understand the change, what it touches, and then restore it deliberately rather than blindly.
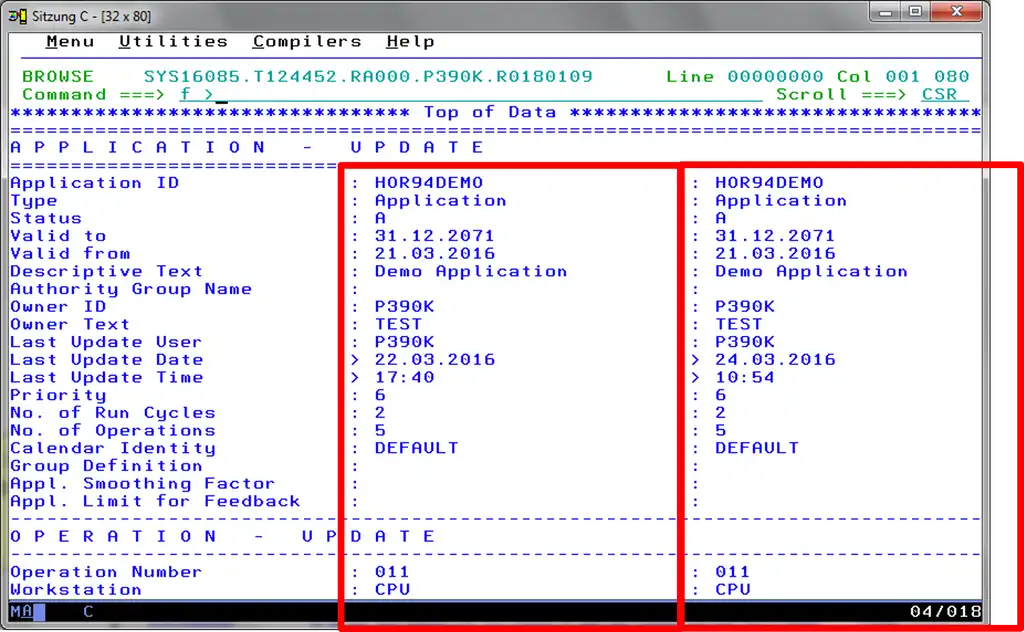
IWS Audit Comparison
From Change Management to Cyber Resilience
Protecting critical systems is about answering four questions when something goes wrong:
What changed?
Who changed it?
What was the last trusted state?
How fast can we recover it?*
The first two support accountability; the last two support resilience. Whether the cause was a compromised account, an insider, or human error, the scheduler now needs to fix it under pressure. Without version history, that means manual reconstruction. With it, incident response looks like controlled recovery instead.
*Note that a recovery and/or an impact analysis depends on the number of applications that were changed, whether the predecessors or successors were also affected, and how long it has been since the data was falsified. Depending on these variables, recovering the correct data can be easy or take time.
Conclusion
Organizations pour lots of resources into protecting mainframe data and applications, but protecting the assets while overlooking the instructions that govern their execution leaves a real gap. IWS can sit at the center of an enormous web of automated processing, and changes to that environment deserve the same visibility, accountability, and recoverability expected everywhere else in the security architecture.
Mainframe scheduling has been treated as background infrastructure for decades, but it's time to give it its own audit trail, version history, and undo button.
See IWS/Audit in Action
Can't yet answer "what changed, and can we restore it when something breaks in your scheduler processes?" Talk to Beta Systems about IWS/Audit.